Establish control
Assign an Incident Lead, use trusted communication channels and engage the right business, legal, insurance and operational stakeholders.
Business email compromise can lead to financial fraud, information exposure, credential theft or access to connected systems. Effective response requires coordinated leadership, communications and technical action.
Business email compromise can begin with a deceptive message or misuse of a trusted digital identity, then develop into payment fraud, unauthorized disclosure, credential theft or access to connected systems. A successful response therefore needs business and technical teams working from the same facts and under clear incident leadership.
Assign an Incident Lead, use trusted communication channels and engage the right business, legal, insurance and operational stakeholders.
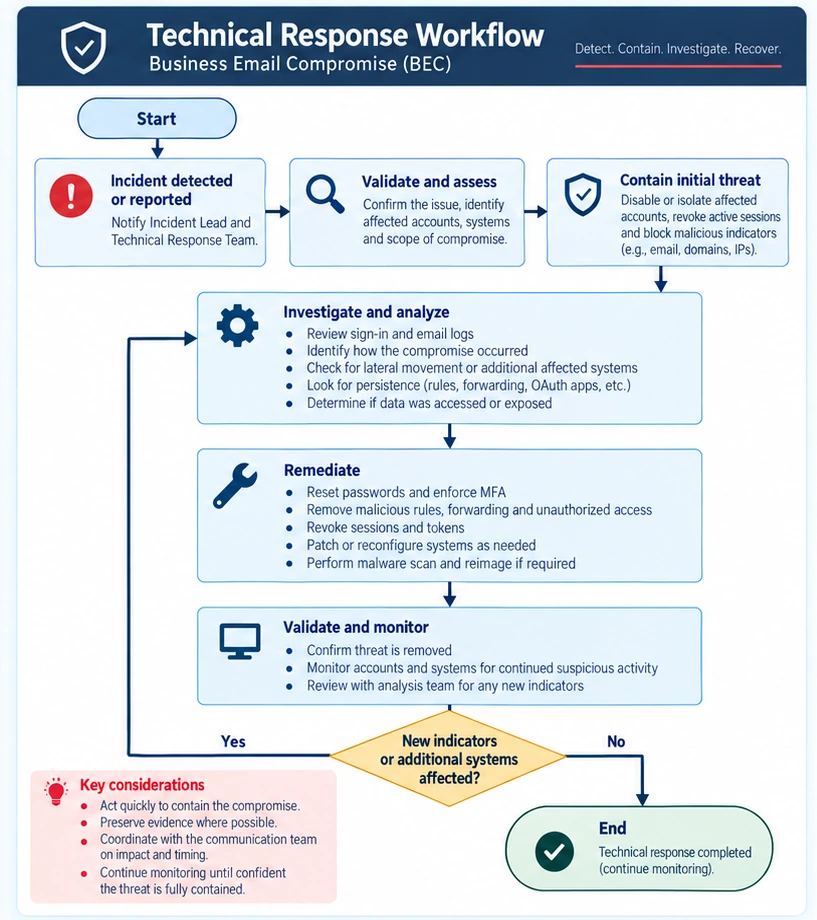
Secure the identity, revoke access, remove persistence, preserve evidence and determine whether the compromise reached other systems or people.
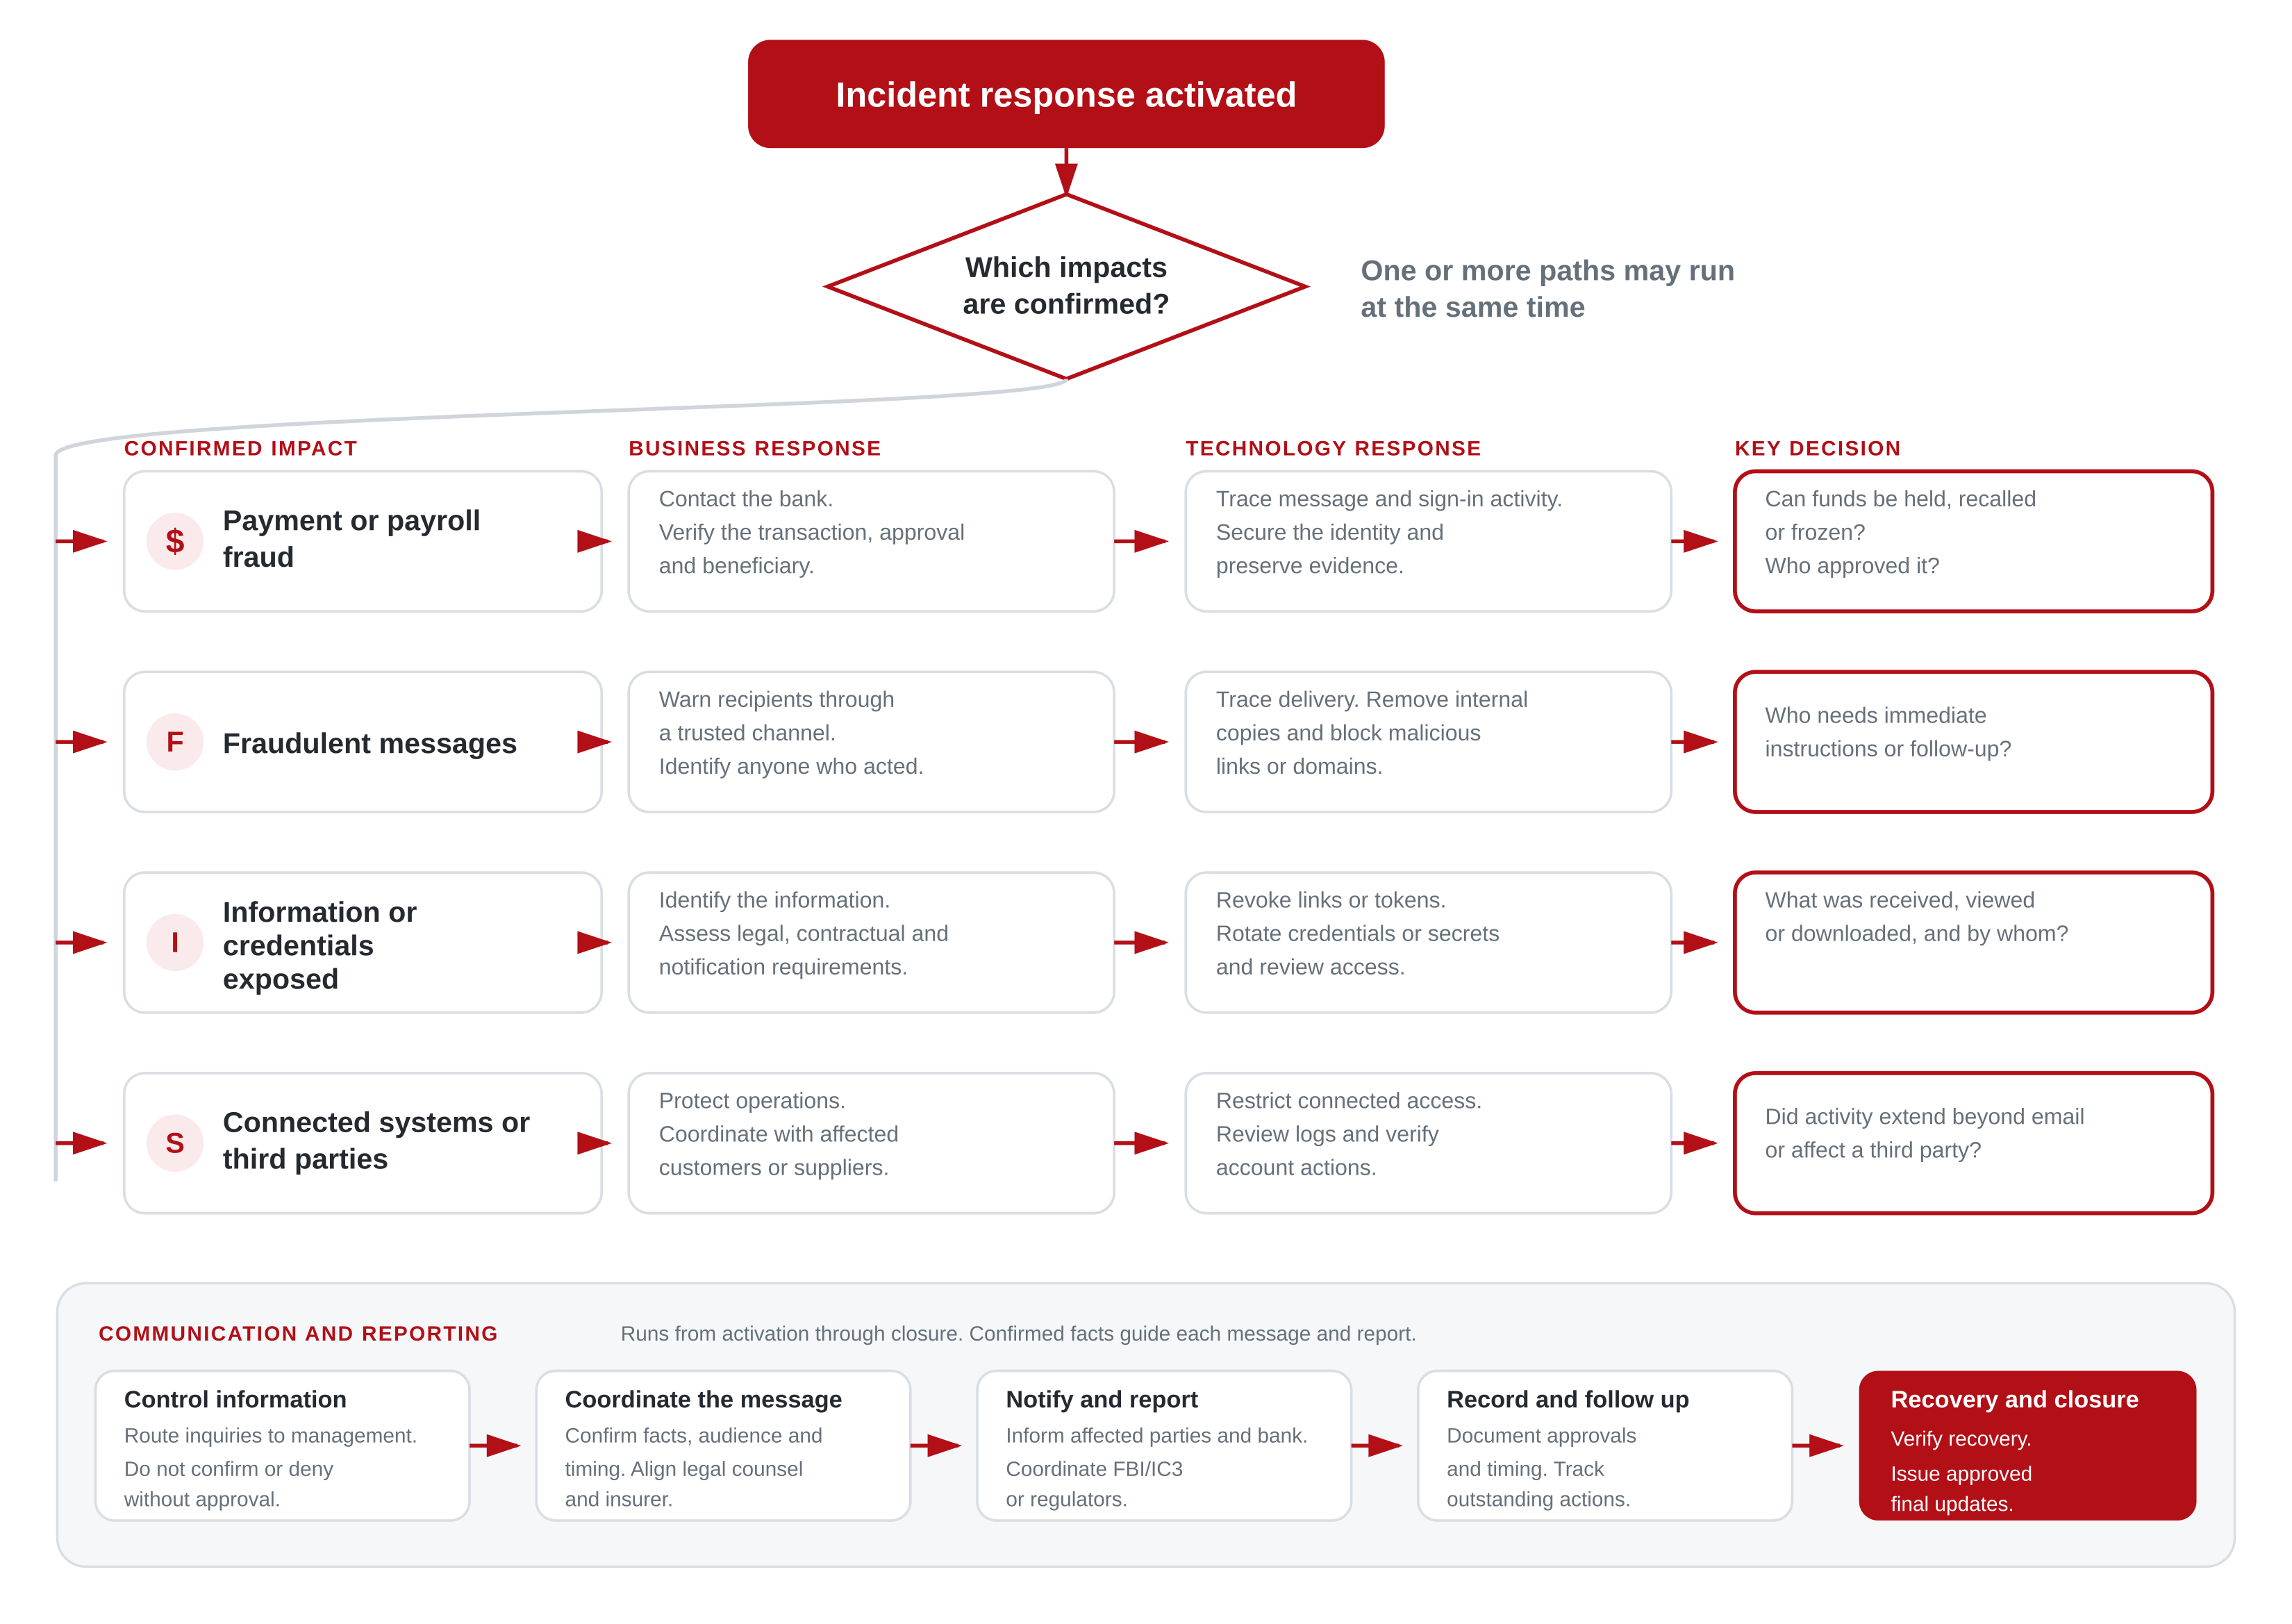
Follow every applicable response path for fraudulent messages, financial activity, exposed information, connected systems and affected third parties.
Verify the account and endpoint, restore access carefully, monitor for recurrence and turn confirmed findings into practical control improvements.
Confirmed impacts may activate more than one response path at the same time. Communication and reporting continue from activation through recovery and closure.
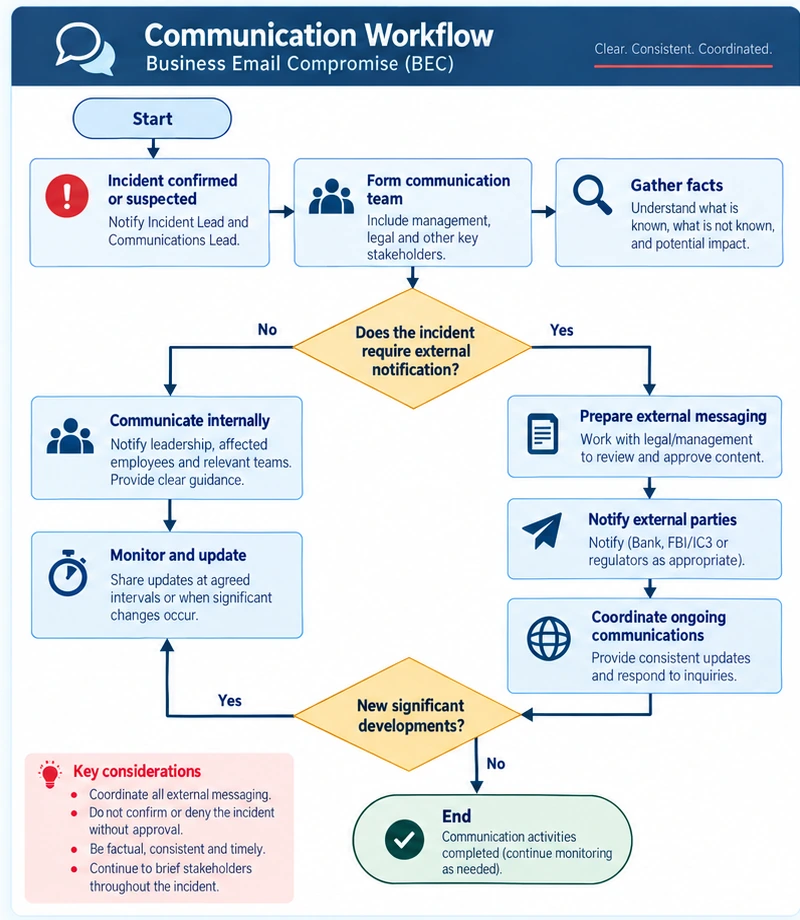
Once the impact is understood, communication and technical response continue as coordinated workstreams. The communication path controls internal and external messaging, while the technical path contains, investigates, remediates and validates the environment.
The post-incident review should address both the technical compromise and the business process that allowed a fraudulent request to succeed. Priorities may include stronger identity controls, email protection, independent transaction verification, endpoint detection, employee awareness, partner procedures and reducing unnecessary access.
Download the full 9-page guide for detailed leadership and communication actions, technical containment and investigation, confirmed-impact response, recovery, prevention controls and official resources.